When Technology Becomes a Question of Trust
A digital service can be fast, polished and still make people uneasy. The discomfort appears when consent is vague, a recommendation cannot be explained, a failed payment has no owner or support feels deliberately distant. Designing trust in technology means giving people understandable choices, proportionate data practices, visible standards, reliable recovery and access to human judgement.
Trust is not a feeling a brand can request. It is a continuing assessment users make from evidence. Every accurate status, reversible choice and resolved exception adds support; every hidden condition or abandoned case removes it. Design can shape those conditions, but it cannot manufacture confidence that operations have not earned.
Designing trust in technology begins with justified dependence
People depend on systems they cannot fully inspect. They need not understand every algorithm or protocol, but they must understand enough to decide: what the service does, what it asks, what could go wrong, what protection exists and who is answerable. Trust grows when dependence is limited and justified.
Separate trustworthiness from familiarity. Repeated exposure can make a pattern feel normal without making it fair. A familiar preselected box, opaque score or difficult cancellation may reduce hesitation while weakening agency. The design question is not “How do we make users trust this?” but “What must be true for reliance to be reasonable?”
Make consequential choices legible
A choice is meaningful when options, consequences and reversibility are clear at the moment of decision. Visual hierarchy should not disguise refusal, urgency should not be invented and the default should not quietly maximise the organisation's benefit. Plain language matters, but plain language cannot repair an unfair choice architecture.
The US Federal Trade Commission report on dark patterns documents interfaces that obscure privacy choices, repeatedly prompt users or emphasise the option that increases data collection. These patterns may improve a short-term conversion metric while teaching people that the interface is an opponent.
Review weight, colour, order, button labels and the number of steps required for each path. Ask a person to explain the consequence after choosing. If refusal requires expert persistence, the presence of a button does not create control.
Collect less and explain the exchange
Every data field creates a promise to protect, maintain and eventually remove information. Start with purpose: why is this detail required now? Could the task work without it, with a less precise form or at a later stage? Data minimisation reduces exposure and simplifies the experience.
The European Commission's explanation of GDPR principles covers purpose limitation, minimisation, storage limitation, accuracy, security and accountability. It also calls for concise, transparent and intelligible information. These are legal principles in a particular jurisdiction, but they also expose useful design questions.
Use layered explanation: a short, specific account at the decision, with detail available without leaving the task. Name recipients, duration and controls. Avoid “to improve your experience” when the actual purpose is advertising, risk assessment or product training.
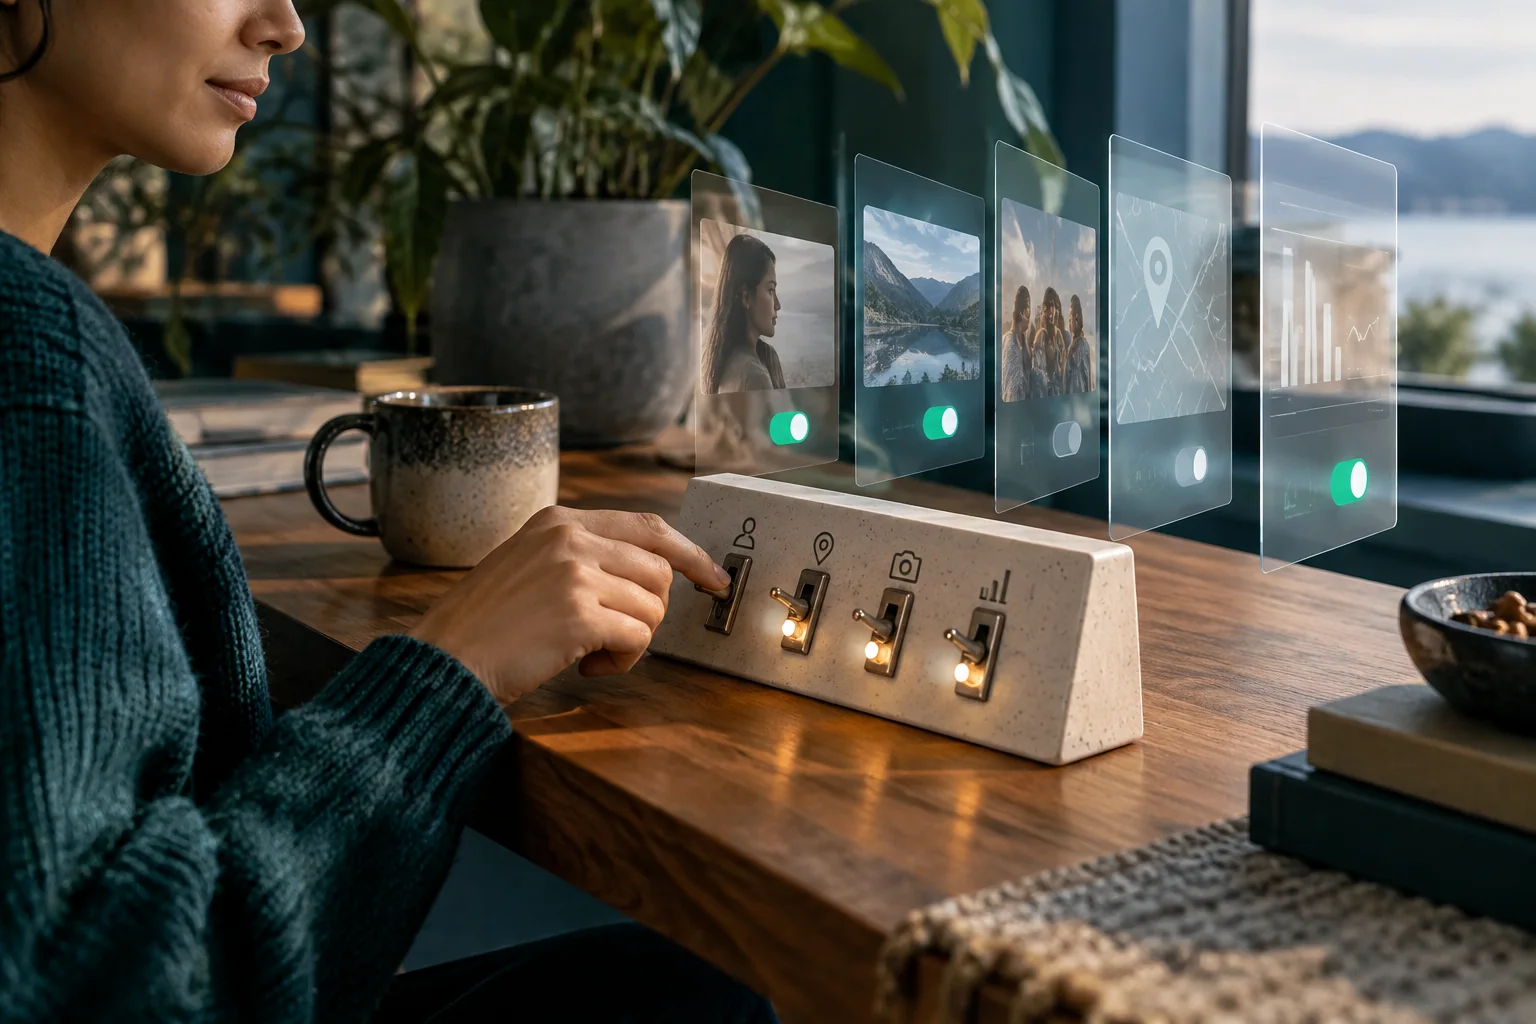
Visible status and specific controls help a person judge what a system is doing.
Verification signals need boundaries
A check mark can refer to identity, qualification, ownership, recent activity or nothing more than a paid tier. Collapse these meanings and the badge borrows certainty. State what was checked, by whom, when and what was not assessed.
Let information expire. Give the subject a correction path and the viewer a reporting route. For ratings, disclose relevant moderation and avoid presenting tiny samples with false precision. Trust signals are decision aids, not guarantees.
This matters for marketplaces and professional platforms, but also internal dashboards. A “low risk” label can influence action beyond its evidence. Show source, freshness and uncertainty close to the result.
Explain automation at the point of consequence
“Powered by AI” says little about a decision. People need to know where automation participates, which information matters, what the output means and what they can do if context was missed. Explanations should support action rather than offer a theatrical view of code.
The European Commission's guidance on rights around automated decisions describes safeguards including human intervention and the ability to contest certain significant solely automated decisions. Product teams should involve legal expertise for applicability; the broader design principle is that consequence requires recourse.
Do not call a review “human” if the reviewer lacks time, evidence or authority to change the result. Measure reversals, reasons and delays. Feedback from appeals should improve the underlying rule, not vanish into case management.
Privacy controls must remain usable later
Consent gathered once does not create lifelong understanding. People need to find settings, recognise what changed, withdraw optional permission and delete or export data where applicable. Use the same language at collection and control.
Design for account transitions: new device, lost number, shared email, death, employee departure and compromised credentials. Privacy can conflict with recovery if identity procedures are improvised. Define evidence and escalation before a vulnerable person is locked out.
The NIST Privacy Framework offers a voluntary risk-management structure for considering how systems affect individuals. A framework does not decide the interface, but it helps connect product choices to organisational accountability.
Reliable service recovery is a trust feature
All systems fail. Trust depends on whether the failure is contained, explained and repaired. A useful error states current status, preserved work, safe next action and expected resolution. It avoids false reassurance and protects against duplicate payment or submission.
Design incident communication before an incident. Decide who can publish status, how frequently updates appear, what channels remain available and how affected people receive final confirmation. Admit uncertainty precisely: say what is known, being checked and when the next update will come.
Compensation or apology cannot replace root-cause work. Group failures, identify who bears the burden and change the system. The analysis in ordinary customer experiences is relevant because recovery often succeeds through messages, handoffs and waiting rather than a dramatic technical fix.
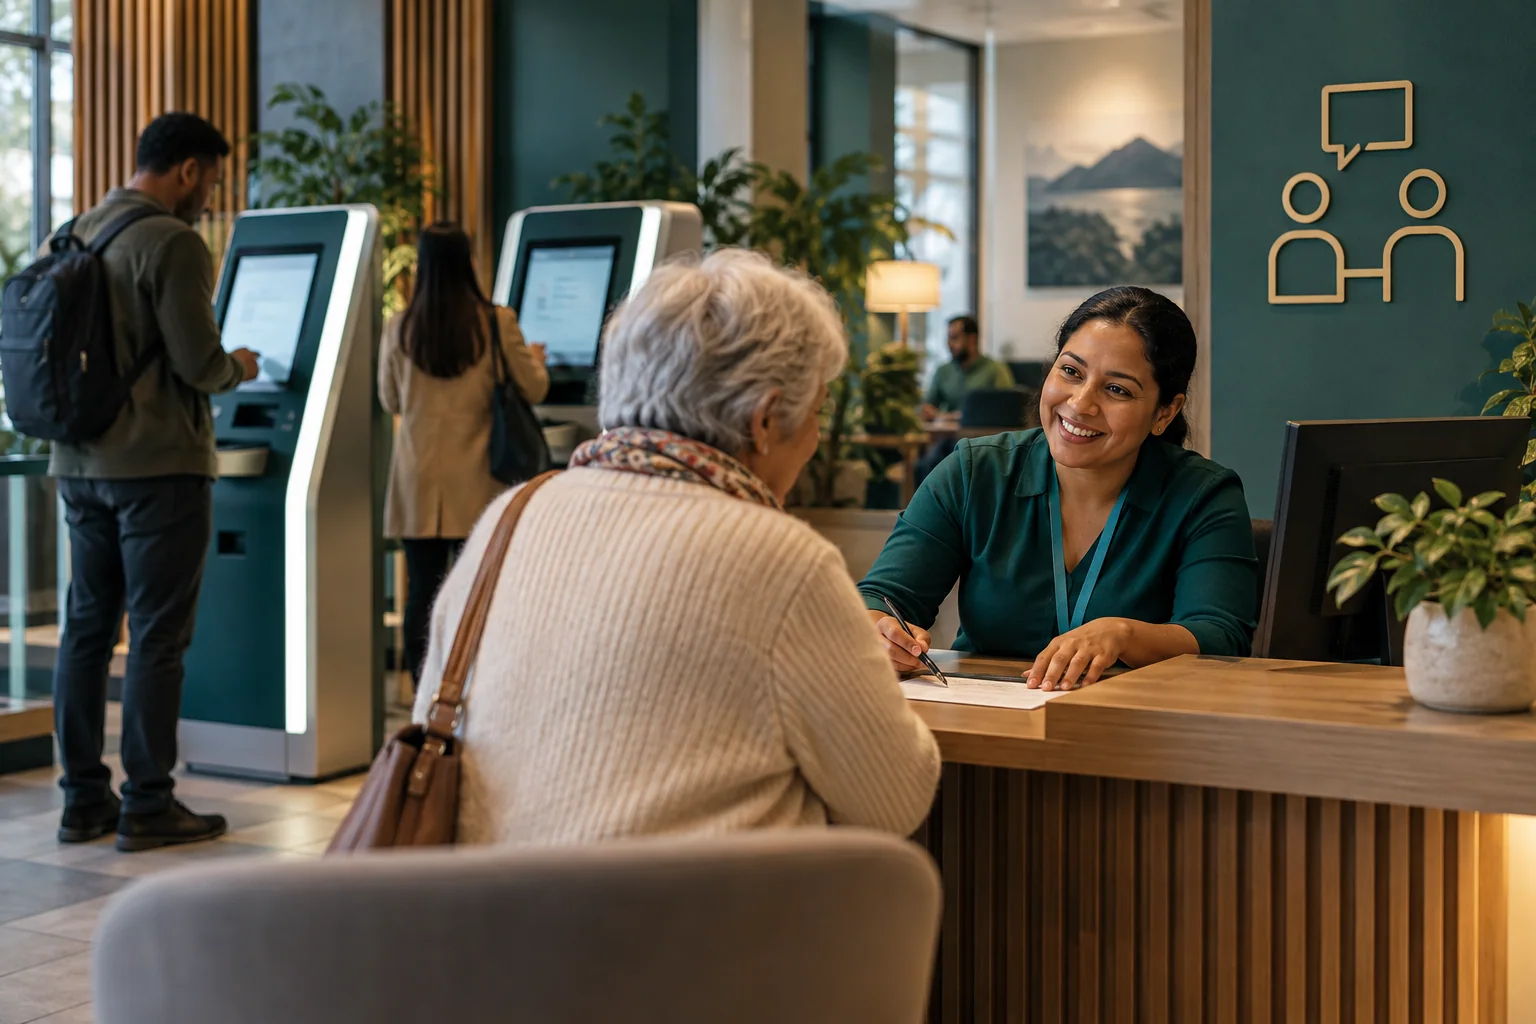
Human support becomes credible when it retains context and has authority to resolve the case.
Human recourse needs access and authority
A chatbot loop is not escalation. Publish a route to a person when safety, livelihood, access or reputation is at stake. Carry the transcript and transaction reference forward. Give support enough context to avoid asking for sensitive information repeatedly.
Authority matters as much as empathy. A polite agent who can only restate the automated answer increases frustration. Define which decisions frontline support can reverse, which require specialist review and how deadlines are monitored. Tell the user who owns the case.
Protect employees too. Provide safe procedures for abuse, sensitive cases and uncertain identity. Trustworthy technology is supported by sustainable human work, not invisible emotional labour.
A twelve-part technology trust review
- Purpose: State the user outcome and organisational purpose separately. If they conflict, redesign the exchange rather than hiding the difference in terms.
- Necessity: Challenge each field, permission and automated inference. Collect the least information and delay requests until they are relevant.
- Choice: Compare prominence, wording and effort across options. Refusal, withdrawal and cancellation must be real paths, not technically present obstacles.
- Comprehension: Test whether people can explain what will happen, including data use, price, renewal, visibility and the limits of a recommendation.
- Security: Bring security expertise into design early. Make protective steps understandable without exposing details that create additional risk.
- Privacy: Map collection, access, sharing, retention and deletion. Give every stage an owner and make controls findable after onboarding.
- Accuracy: Show source and freshness where they affect judgement. Provide correction for profile data and a response path for disputed content.
- Automation: Identify decisions influenced by models or rules. Explain consequence, monitor unequal errors and provide qualified review where needed.
- Status: Distinguish submitted, pending, completed, failed and reversed states. Synchronise customer and support views so the organisation tells one truth.
- Recovery: Preserve work, prevent duplication, communicate timing and assign a case owner. Test incidents and offline fallbacks before release.
- Exit: Make cancellation, export, deletion and account closure understandable. State what remains, why and for how long.
- Governance: Record decision owners, evidence, known limits, monitoring and review dates. Give risk, legal, design and frontline teams routes to raise concern.
Run the review on a realistic journey, not a slide. Include someone who represents customer support and someone independent of the growth target. Record unresolved questions as risks with owners. A green checklist without evidence is another trust signal the organisation has not earned.
Measure behaviour without reducing trust to a score
No single metric measures trust. Use completion, informed refusal, withdrawal, correction, disputed decisions, recovery time, repeat contacts and complaint outcomes. Review security and privacy incidents alongside customer evidence.
High acceptance can indicate value or manipulation. Low complaints can indicate satisfaction or inaccessible recourse. Pair metrics with comprehension testing and interviews. Look for differences across language, device, disability and other relevant contexts while respecting minimisation.
Measure the organisation's behaviour too: overdue access requests, expired data, unresolved appeals and time to correct inaccurate status. Trustworthiness is more actionable than sentiment because teams can own it.
Align the brand promise with the product's power
A brand voice that says “you are in control” is contradicted by hidden settings. A promise of simplicity is contradicted by a maze after failure. Product, policy, support and communication need one account of what people can expect.
This is where digital platform design and brand strategy meet. Marketing should not outrun the protections in the service. Conversely, well-designed control should be explained rather than buried in legal language.
The ethical interface explored in interfaces that make room for doubt offers a useful principle: allow comparison, hesitation and reversal when a decision deserves them.
Test trust through difficult scenarios
A happy-path usability session cannot show whether a service deserves reliance. Add scenarios that expose power, uncertainty and failure. For each one, observe comprehension, control, staff capability and the final state of the case.
A permission is refused
Ask a participant to decline analytics, location, contacts or marketing while completing the core task. Check whether labels are neutral, refusal persists and the service still works as promised. Watch for repeated prompts that turn a decision into endurance. Confirm that support sees the same preference and does not ask for an unrelated permission.
A person changes their mind
Withdraw a consent, cancel a renewal or revise a submitted choice. The control should be findable from the place a person expects, use the same vocabulary as onboarding and explain consequences before confirmation. Verify what changes immediately, what takes time and what information must remain for a legitimate reason.
The connection disappears
Interrupt the network during upload, payment and confirmation. The interface should distinguish a local connection problem from a known service failure, preserve safe work and avoid encouraging duplicates. When connectivity returns, status must reconcile across the customer's device, transaction system and support view.
A recommendation is wrong
Present a plausible error in a recommendation, risk label or automated classification. Can the person see that the output is advisory or decisive? Can they correct the input, add context and reach qualified review? Record whether reviewers can actually change the result and whether the system learns from a confirmed error.
A verification expires
Use a provider whose credential is no longer current. The interface should not display a timeless badge. It should show status, relevant date and what the check covered. Test alerts to the provider, protection for existing customers and the route for renewed evidence without exposing sensitive documents.
A device is shared
Complete the journey on a phone or computer used by other people. Examine previews, saved sessions, autofill, account switching, downloads and sign-out. A convenience feature can become disclosure. Let the user decide what persists and avoid revealing sensitive subjects in notification text.
A phone number is lost
Try recovery without access to the original device or SIM. Security must resist takeover without permanently excluding a legitimate owner. Explain evidence, review timing and escalation. Avoid support improvisation that asks people to send excessive identity documents through insecure channels.
A payment remains pending
Keep the transaction unresolved beyond the normal estimate. Show amount, recipient, current status and what not to do. Send a proactive update and give support the transaction context. Test reconciliation, reversal, refund and final confirmation, including what happens when partners disagree.
A complaint challenges the system
Submit a complaint about the rule, not only a single case. Ensure it reaches governance rather than disappearing after compensation. The response should name the decision, evidence and available review. Aggregate similar complaints while protecting individuals, then track whether the underlying product or policy changes.
A service provider fails
Simulate an outage or breach at a critical supplier. Customers should not have to understand the contract map to get help. Define which organisation communicates, resolves cases and provides records. Test whether internal teams can see affected transactions and whether the vendor agreement supports the recovery promise.
A vulnerable person asks for help
Use a scenario involving coercion, bereavement, accessibility or financial hardship. Scripts should guide without forcing disclosure to multiple agents. Provide private channels, specialist escalation and appropriate pace. Measure whether safety controls unintentionally remove agency or make the person prove vulnerability repeatedly.
The organisation must say it does not know
Present a novel failure without a reliable estimate. Teams should communicate uncertainty precisely, avoid speculation and commit to the next update. Test who authorises public information and how corrections appear. Honest uncertainty with a dependable rhythm is more trustworthy than a confident deadline that repeatedly moves.
After testing, connect interface findings to policy, data, staffing and supplier decisions. A label change may improve comprehension, but it cannot solve an appeal team without authority or a payment rail without reconciliation. Trust review ends only when the operating condition changes.
Govern trust claims with evidence
Words such as secure, private, verified and transparent are claims, not decoration. Create an evidence owner for each one. Record the technical or operational control, its scope, last review and the language approved for public use. Remove or qualify a claim when the evidence changes.
Keep marketing, product, security, privacy, legal and support aligned. A security certification may cover one system, not every partner or user action. A verified profile may confirm identity but not competence. Precise limits make communication more believable and help customers decide appropriately.
Review claims after incidents and major releases. Ask whether the interface still describes reality, whether support can explain the protection and whether a reasonable person could misunderstand its boundary. This discipline lets a brand communicate genuine strengths without turning complex safeguards into absolute promises.
Document every exception that changes a person's rights or access. The governance practices behind a coherent identity help product, policy and communication teams keep the same account of control.
Designing trust in technology is continual work
- Designing trust in technology* means reducing unjustified dependence and increasing understandable control. It connects privacy, accuracy, human recourse and service recovery to the actual moments where people decide whether to rely on a system.
Begin with one consequential journey. Write what the person must know, choose, contest and recover. Test the failure state with the same care as onboarding. Assign owners to the promises the interface makes. Trust will not arrive as a launch asset; it will accumulate when the service behaves honestly, especially when something goes wrong.
Author

Kettely BLARY
Kettely Blary is a founder with a distinctive approach, driven by a deep interest in how ideas evolve—from their earliest spark to their full realization in the tangible world. The author of To Make a Faun Sit and Mapipis, she explores in both her writing and her projects the moment when intuition takes shape—when something abstract becomes real and embodied. As the head of KB Ayilink, she develops and leads projects that carry ideas beyond their original scope. Her work reflects a strong sense of balance between structure and movement, intention and execution, and individual expression and collective dynamics. Across everything she does, she is guided by a simple belief: ideas truly come into their own when they find their most compelling form in the real world.